New feature in PIM - fire custom extensions on role activation
Add custom business logic to PIM role activation requests with custom extensions
Field notes, honest opinions and practical guides about Microsoft Entra, identity governance and cloud security.
Explore the notebook
Add custom business logic to PIM role activation requests with custom extensions
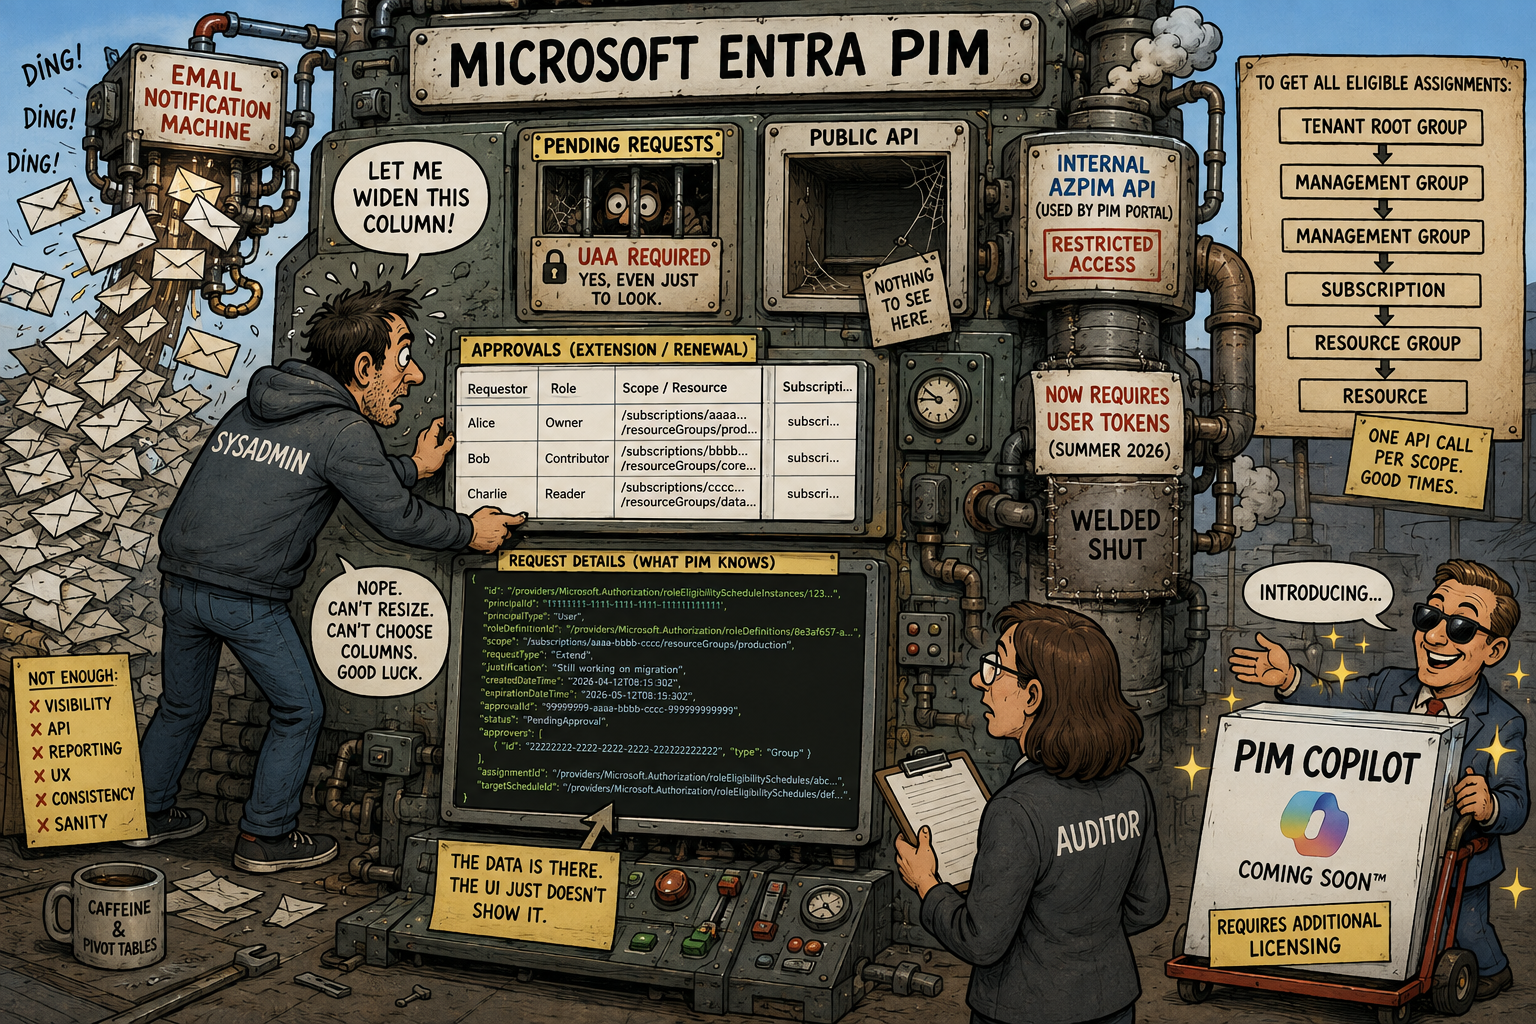
If Microsoft made me Product Manager of PIM for a day, here's what I'd put on the backlog.
Microsoft has just released a hot, new feature in their cloud IGA offering, Entra ID Governance (Entitlement Management), allowing request on-behal...
Gain insights for security and compliance reasons by reporting on all service principals in Entra ID (former Azure AD) having Microsoft Graph app R...
Securing identities in Azure AD with MFA is a no-brainer, but is it really enough? Let's look at attack vectors for the various MFA methods, and ho...
Utilizing PIM and having no active privileged Azure RBAC or Azure AD roles by default, always requiring 'just-in-time' elevation, is an important r...
In today's threat landscape it's important to be healthy paranoid and always re-think how attackers could potentially breach an organization's defe...
Keeping an eye on Azure AD administrative role assignments is crucial for tenant security and compliance. Forget about the built-in PIM report in t...
Kusto Query Language (KQL) is a powerfull tool to query Azure AD log entries from Log Anayltics in Azure. See how you can query log data using Powe...
Workload identities, meaning apps, managed identities and other service principals, can be granted tenant-wide application access to all mailbox re...
Microsoft Graph and SharePoint Online supports some granular access permissions using Sites.Selected application scope in Graph, and app access rol...
Managed Identities can be used instead of app client secrets and certificates for Azure resources authenticating to Azure AD. Let's look at what a ...
Let's look at how to configure access to Azure Storage Blobs using Attribute-based Access Control (ABAC) paired with Custom Security Attributes
Let's look at blocking legacy authentication protocols in a global company's Azure AD with full control and ease of mind
This blogpost explores the new Custom Security Attributes public preview feature in Azure AD
Microsoft released a new public preview feature for Azure AD Identity Governance during Ignite this week, namely Custom Extensions for Entitlement ...
Learn how to add custom extension attributes to Azure AD objects
Let's go from zero to somewhat hero by getting familiar with topics like REST API, JSON, HTTP methods, access tokens, permission scopes, Graph Expo...
The second blogpost in the series explains the Microsoft Graph.
The third blogpost in the series explains the Graph Explorer.
The forth blogpost in the series explains the Graph Powershell SDK.
My first-ever blog post walks through how to configure automated user provisioning and single-sign-on from Azure AD to SaaS apps, specifically for ...
No articles found. Try another search.